Monday, February 15, 2010

Asterisk Dialstring Injections

It's like an SQL Injection attack, trying this one now on my VoIPSec lab. Time to fix those Asterisk cookbooks guys! - Ron

[from_sip]
exten => _X.,1,Dial(SIP/${EXTEN}@testsip)
He writes: “And if ${EXTEN} = “000@testsip&SIP/333” what turns out to happen then is similar to SQL injection :-(  ”He is exactly right. Many VoIP protocols, including IAX2 and SIP, has a very large allowed character set in the dialed extension, a character set that allows characters that are used as separators to the dial() and the queue() applications, as well as within the dialstring that these applications send to the channel drivers in Asterisk. A user can change the dial options and dial something we should not be able to dial in your system. This article describes the issue in more detail and gives you some help on how to avoid this causing trouble in your Asterisk server.
complete technical details here:  http://www.voip-forum.com/?p=241&preview=true

Sunday, February 14, 2010

CloudAudit A6 - The Audit, Assertion, Assessment, and Assurance API

CloudAudit and the Automated Audit, Assertion, Assessment, and Assurance API (A6)

The goal of CloudAudit (codename: A6) is to provide a common interface that allows cloud computing providers to automate the Audit, Assertion, Assessment, and Assurance (A6) of their infrastructure (IaaS), platform (PaaS), and application (SaaS) environments and allow authorized consumers of their services to do likewise via an open, extensible and secure interface and methodology.

CloudAudit is a volunteer cross-industry effort from the best minds and talent in Cloud, networking, security, audit, assurance and architecture backgrounds.

The CloudAudit/A6 Working group was officially launched in January 2010 and has the participation of many of the largest cloud computing providers, integrators and consultants. You can find out more about CloudAudit by visiting the Forums.

For someone involved in the Cloud Computing industry, information assurance and compliance, this is freakin' awesome! I would like to congratulate everyone involved, especially security guru and fellow-grappler Chris Hoff (Cisco) of rationalsurvivability.com

Find more about the A6 initiative at http://www.cloudaudit.org/ and please spread the word!

Thanks,
Ron

Saturday, November 21, 2009

"New Moon" Movie Now Playing on Torrent Sites

Capitalizing on the Team Edward versus Team Jacob fever, a couple of New Moon.avi movie files are now appearing on well-known torrent sites. Of course its not the real thing, opening the actual .avi file redirects you to cleverly crafted website, www.microsoftmedicenter.com. Yes kids, look closely before you click:


Its mediacenter, minus the letter "a". Good job guys, but its an old trick, only works for kids and those who do not practice safe Internet use in the first place.

I found out about this from a friend who IM'ed me that I need to fix his laptop again because he caught a nasty virus or something for the Nth time this month. He told me the last thing he did was simply open an .avi movie file that redirected him to Microsoft's website and that's when thing started to act funky.

The problem is that this guy never listens. He downloads a lot. He refuses to pay for music and movies. Downloading illegal copies of media is hurting the industry. And nothing is free in this world, download a free new movie, get a free evil payload (virus, adwares, scarewares, etc.)

So I inspected his laptop and immediately browsed to the New Moon Movie folder. Everything looks legit, you can even do a quick scan of the .AVI file using Microsoft's Security Essentials and no alerts came out.

So off I go and I opened the movie and as expected my browser popped open and gets directed to www.microsoftmedicenter.com.

However, what I got was a Bandwidth Exceeded return error. Hopefully someone DDoS'ed his website for good, or it got taken down already, or this guy is indeed maxing out the allotted bandwidth for his website because his clever trick is working.

Bandwidth Limit Exceeded The server is temporarily unable to service your request due to the site owner reaching his/her bandwidth limit. Please try again later.
Apache/2.2.11 (Unix) mod_ssl/2.2.11 OpenSSL/0.9.8e-fips-rhel5 mod_python/3.3.1 Python/2.4.3 mod_bwlimited/1.4 PHP/5.2.6 Server at microsoftmedicenter.com Port 80

So I made my part as good Netizen of this world and decided to explore and learn more about this poorly-spelled website. First stop is a back trace to see where this guy is hosted:

Wow, Amsterdam, land of the free. If it is indeed hosted in that country. Let's try a whois test:

http://whois.domaintools.com/microsoftmedicenter.com

Here's what we know about microsoftmedicenter.com:

* "James Gonzaga" owns about 13 other domains View these domains >
* is a contact on the whois record of 3 domains
* 1 registrar has maintained records for this domain since 2009-05-14
* This domain has changed name servers 3 times over 0 year.
* Hosted on 4 IP addresses over 0 years.
* View 49 ownership records archived since 2009-05-16 .
* Wiki article on Microsoftmedicenter.com
* 193 other web sites are hosted on this server.

DomainTools for Windows®

Now you can access domain ownership records anytime, anywhere... right from your own desktop! Find out more >
Registrant:
James Gonzaga
Roxas Boulevard
Manila, NCR 2000
Philippines

Domain Name: MICROSOFTMEDICENTER.COM
Created on: 14-May-09
Expires on: 14-May-10
Last Updated on: 27-Oct-09

Administrative Contact:
Gonzaga, James
Roxas Boulevard
Manila, NCR 2000
Philippines
+63.9194341212 Fax --

Technical Contact:
Gonzaga, James
Roxas Boulevard
Manila, NCR 2000
Philippines
+63.9194341212 Fax --

Domain servers in listed order:
NS1.WATCHUNDERGRADS.COM
NS2.WATCHUNDERGRADS.COM


And the plot thickens! Domain name was registered to a fellow-Filipino residing in Manila? Who knows. Unless Domain Name registration requires a high-level of authentication and presentation of credentials, I doubt if there is even a James Gonzaga along Roxas Boulevard in Manila. I am going to try that listed Philippine number in some other time, who knows, maybe there is a real James Gonzaga prowling the streets of Manila.

If someone picks up, I will ask "Is this James? Can I pay in $$$ and distribute some of my stuff on your website and be part of my worldwide BOT NET operation?"

Evil grin. That's how easy bad guys do transaction with smart kids from developing countries. All they need to do is mention the word US Dollars.

Next stop is let's NMAP this baby, I don't care if he backtracks on my trace, I make sure I cover my tracks:

Hmm, a couple of filtered interested ports. Maybe next time.

Stay tuned.

Friday, October 16, 2009

Thawte dumps free personal E-mail Certificates

Important Thawte&reg Personal E-mail Certificate Holder Notice

Thawte Personal E-mail Certificates and Web of Trust are being discontinued

Dear (My Complete Full Name - PacketBoy),
Over the past several years, security compliance requirements have become more restrictive, while the technology infrastructure necessary to meet these requirements has expanded greatly. Despite our strong desire to continue providing the Thawte Personal E-mail Certificate and Web of Trust services, the ever-expanding standards and technology requirements will outpace our ability to maintain these services at the high level of quality we require. As a result, Thawte Personal E-Mail Certificates and theWeb of Trust will be discontinued on November 16, 2009 and will no longer be available after that date.

Deciding to conclude these services was a difficult decision for us to bear, specifically because of the community that has been built around these products over the years.

To express our gratitude and sincere appreciation for being a part of our Thawte community, we would like to offer you up to $100.00 off the purchase price of our SSL and/or code signing certificates.

If you would like to take advantage of our offer, please forward this email to our sales department. Their contact details are listed at the foot of this message. Please note that this offer expires on November 16, 2009.

We have also made a special arrangement with VeriSign regarding replacing your personal email certificate. VeriSign's exclusive offer to you is for a FREE 1-year replacement personal email certificate - a $19.95 value. This offer will be open for 2 months after the service is discontinued and will no longer be available after January 16, 2010. Simply follow appropriate link below to request your certificate:

MS Internet Explorer:
https://digitalid.verisign.com/client/class1MSToken.htm

For Mozilla, Firefox, Netscape, or Apple Safari:
https://digitalid.verisign.com/client/class1NetscapeToken.htm

You may replace each of your active certificates with a VeriSign® Digital ID for Secure Email using the following token(s):

A3067904AD83FDD2B34E76631A09A178

Click here to receive answers to questions you may have with regard to enrolment for and installation of your free VeriSign Digital ID class 1:https://search.thawte.com/support/ssl-digital-certificates/index?page=content&id=SO12704

For answers to further questions you may have about the discontinuation of this service and the impact to your existing certificates please refer to the following FAQ:https://search.thawte.com/support/ssl-digital-certificates/index?page=content&id=SO12658
(we will keep this FAQ updated with responses to common questions)

We hope we can keep you in the Thawte family as customers of our SSL and code signing products. Thank you for your support of Thawte Personal E-mail Certificates and Web of Trustover the years.

Kind regards,

Thawte Technical Support
E-Mail: personalcert@thawte.com
FAQ: Click here for FAQ

If you would like to take advantage of our free SSL and code signing offer, please forward this email to our sales department using the details listed below:
North American Sales
Tel: +1 888 484 2983
E-Mail: us-sales@thawte.com

Online Chat: Click Here to Chat
International Sales
Tel: +27 21 937 8902
E-Mail: int-sales@thawte.com

Online Chat: Click Here to Chat

Tuesday, October 13, 2009

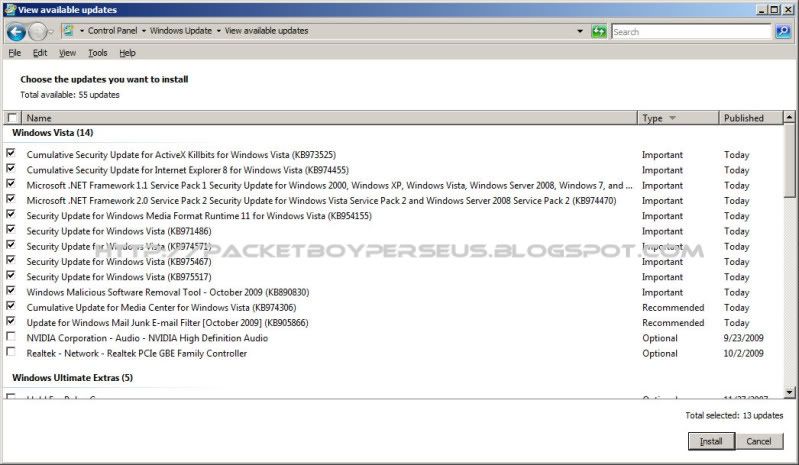
October 13, 12 Updates for my Vista box, 1 Goal: Security


I would like to thank Dungeons & Dragons Online MMORPG for giving me a reason to play around with my Lenovo SL300 again and at the same time discover the multiple security updates for Vista released today by Microsoft.

This laptop has been sitting around gathering dust for a while. Simply because I hated the bundled Windows Vista Ultimate Sp2 OS. I would consider it a moderate-gaming laptop, with a dedicated Nvidia 128mb graphics chip. I rarely open this laptop, save for occasions where I need to do cross-Windows OS platform compatibility and User Acceptance Testing (UAT) of our proprietary VoIP application.

Another reason I boot it up is just to make the Avira Free Anti-Virus and Spybot S&D definitions updated, and of course, checking for Windows Updates is critical and has always been a routine for me every time I boot up my Windows systems, and any Windows systems I play around with regardless if I have it set to acquire Automatic Updates.

Today, October 13, after getting tired of completing Rank 2 Quests for my female Monk character (Yes, shame on me, my account in DDO is VIP) I decided to log out of my alternate universe, head back to the real world and work on my Security+ reviewers and SANS Institute Reading Room materials.

Jumping from one security website to another is a good alternative method to review. Sometimes staring and reading a book with 1000 pages will bore you one way or another, and you will want something more interactive.

One of the websites I frequently visit is Threatpost.com, a relatively new site which I find very enjoyable to read. Not 2600'ish, but the articles and pictures are very enticing. The white page background and colorful graphics on this website makes the hardcore articles look like easy-reading, hence the enticing factor.

Threatpost also scales well on my Blackberry 8330's screen; as well as this humble blog of yours truly. Please go and try it. I find it very convenient to just pop-out my smartphone and read along every time I ride the BART going to work. Keeps me updated on the current IT security news. It's like Slashdot but only with Security-related topics.

Back to my Vista Ultimate SP2 box and its merry 12 updates from Microsoft on a single day, here's a screen shot of the list (click on thumbnail to enlarge screen shot)


Just by looking at these KB numbers I am already having headaches :-) Head to Microsoft's Security Bulletin website to find out what each Knowledge Base (KB) is all about:
http://www.microsoft.com/technet/security/current.aspx

You may want to try and use Microsoft's Baseline Security Analyzer on a couple of your Vista boxes. Just to make sure your Vista boxes, your brother's, your sister's, even your friend's friends Vista boxes are updated and safe.

Vista is beyond SMBv2 exploit (MS0-9050) nowadays, it has been a haven of choice for wannabe hackers and script-kiddies.

I wonder what's going to happen with Vista with Windows 7 coming out in a few days. Will it be the new Windows ME in memory?

Play safe kids.
Ron


Wednesday, October 7, 2009

Poor City Planing and your Disaster Recovery Plans


T
he Philippine Government finally admitted that poor city planning was the root cause of the recent massive flooding claiming the lives of nearly 300 people near and around the City of Manila.

Growing up in the Philippines, it doesn't take a genius to figure this out. We do not need statistics or blueprints of how the city was designed to scale presented to us to understand this.

You see it and you smell it.

I hate to say the "smell" thing because its very unlikely to come out from a patriotic Filipino guy like me, but it is the truth at least in my experience and opinion. Some part of Metro Manila is so congested that you do not need to open your eyes to know that this area is overpopulated.

You can't blame those people. Healthy conditions are the least priority of people who rarely eat at least twice a day and needs a shelter at night. Celebrities and politicians residing in tall buildings were not spared as well by the flood. There was even a story circulating around of a "dashing" rescue, worthy of a movie, wherein a famous actor rescued an actress in distress from her tall residential building using a speedboat. And not helping the less-privileged neighbors.

In the corporate IT world, I can almost imagine the feeling of helplessness of the people in charge of the Disaster Recovery and Business Continuity Plans (DRP & BCP) for their respective organizations.

These guys, mostly the Senior Network Administrators and Chief Security Officers of the corporate world, spent hundreds of man-hours in designing, testing, and implementing plans to
disaster-proof their business, regardless if its a natural or man-made disaster. The basic and ultimate goal is to survive such events and still continue to do business.

The problem is the actual city where your network infrastructure and organization is physically located. If the city was not designed with security, room for growth, and disaster recovery in mind, your plans get tossed out of the window.

Major City planners of the world should take a page out of secure software developers book: Design with security in mind. And spend less time mitigating risks.

If your city gets flooded to the point that major streets and thoroughfares look like a wild, gushing river, your well-laid plans most likely will take a detour. This detour is where your plans will be actually tested because you do not know whats going to happen next.

However, on major events like this, disaster recovery and business continuity plans should be tossed out of the window for the time being and self-preservation and helping other lives should be the number one priority.

After securing the lives of people working for your organization, go out and help out. Events like this happen for a reason and it makes organizations and cities plan and prepare better for the future.

Lessons learned is always the last phase of such events. Take detailed notes, recall how the event escalated, and learn from your mistakes.

Monday, September 21, 2009

PDF Reader Risk Mitigation and Herd Mentality in IT Security Best Practice

The prevailing trend for security conscious system administrators and IT personnel nowadays regarding the risks that Adobe Acrobat PDF reader presents in the network is to dump the entire PDF reader application in favor of another.

This trend is an attempt to accomplish Risk Avoidance. Risk Avoidance is a Risk Management Method wherein you terminate the activity that is introducing the risk. In short, no need to implement and keep track of your Risk Mitigation process since there is nothing to keep track of in the first place. No Adobe PDF Reader, no risk. And why worry about Adobe PDF Reader Zero-Day exploits when you can use another PDF reader that is not affected by such vulnerabilities? Ok, that sounds logical and you may have a point Mr. IT Admin Sir, but please listen.

Enter Foxit PDF reader, the leading candidate and alternative for Adobe's dominant PDF Reader. However, converting your entire company to Foxit PDF reader does not guarantee 100% Risk Avoidance. The Top 2 misconceptions about Foxit PDF Reader are the following:

1. Foxit PDF Reader does not have Javascript (Who needs Javascript on a document reader anyways?!)

>False. Foxit PDF Reader (the most recent version in time of this writing is 3.1.1.0901) also has Javascript and as a matter of fact, is also enabled by default during first installation. So go ahead and disable that damn Javascript by going to Tools>Preferences>Javascript and remove the check mark to disable it.

2. Foxit PDF Reader doesn't have exploits and vulnerabilities like Adobe PDF Reader.

>False. Although Adobe PDF Reader leads in scoring when it comes to exploits and vulnerabilities (Like 10 Exploits Adobe PDF Reader, and 2 Exploits Foxit PDF Reader) Foxit has its own share of bad apples. From Buffer Overflow Exploit to Remote Denial of Service Exploit, yes, Foxit is also prone to PDF-related exploits and vulnerabilities.


It won't take long for malware authors and security researchers to create new and more exploits targeting alternative PDF readers such as Foxit PDF Reader. The same rule applies when dumping Adobe PDF Reader in favor of another; patch your applications and systems on a regular basis, keep tab of Zero-Day exploits. Enforce your company or organization Policies, Standards, Baselines, Guidelines and Procedures to the full extent but not to the point that you lose your sanity in the process, and your co-workers start tagging you as control freak.

Although I find random on-the-spot, casual conversation, Security Awareness Training the best tactic one can employ inside the workplace. So every morning, while lining up for coffee at the pantry room, go ahead and break some "cool" and "leet" IT security news to your fellow workers, they will enjoy it as long as you tell the story like how movies tell them. Avoid jargon and acronyms please and make it exciting. Think Quentin Tarantino directing a hacker-movie.

Bruce Schneier made an excellent point on his speech about "The Future of the Security Industry: IT is Rapidly Becoming a Commodity" on a recent OWASP Meet. Bruce mentioned that the trend nowadays with IT security is slowly turning into a somewhat herd mentality. They are doing it, so let's do it, that kind of thing. Even current Best Practices recommended by the community is suffering from such herd-mentality syndrome. I somehow agree on this notion since everywhere I go and every material I read describes a Best Practice guide which usually doesn't always apply to all.

We need to treat each system, no matter how closely it resembles other systems, as a unique system with a different set of variables and behavior. So please, stop treating those Best Practice Guides as your bible and study your network how it behaves.

Cheers!
Ron


Sources:
1. "Handling Risk" Page 107, Chapter 3: Information Security and Risk Management, All-in-One CISSP Exam Guide 4th Edition by Shon Harris, CISSP, MCSE
2. Bruce Schneier: The Future of the Security Industry: IT is Rapidly Becoming a Commodity, http://vimeo.com/groups/owaspmsp/videos/6495257
3. Open Web Application Security Project (OWASP), http://www.owasp.org/index.php/Main_Page
4. http://www.schneier.com/

A playground for network security enthusiasts, innovators and early adoptors


Welcome to my blog, this is me thinking out loud about Voice over IP security (VoIP), managing and optimizing converged networks, Metasploit Framework, Cloud Computing, general security and privacy concerns, grappling adventures, and tuning my MKIV VW Jetta.

All inputs, feedbacks and violent reactions are welcome.

Packet Boy Perseus
Helping spread a positive image why we hack things.

About Me

I am an InfoSec Innovator, a Blue Ocean Seafarer and a Paul Graham Pupil.